THE AGENTIC SECURITY CONTROL PLANE
Discover AI maps every agent, tool, MCP, and Skill in your environment. Ascend AI attacks them autonomously to find what actually breaks. Defend AI blocks agentic threats at runtime. The AI Agent Kill Switch takes rogue agents offline in seconds.
The Problem
An agent holds credentials, calls tools, reads data, and decides what to do next on its own. That is what makes it useful, and it is what makes the attack different. The agent rarely goes down. It gets convinced to act on someone else's behalf, using permissions you gave it.
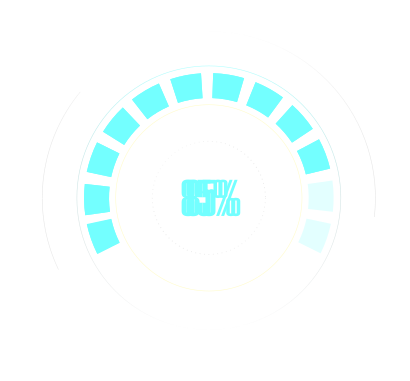
of successful attacks caused an agent to silently do something it was never authorized to do
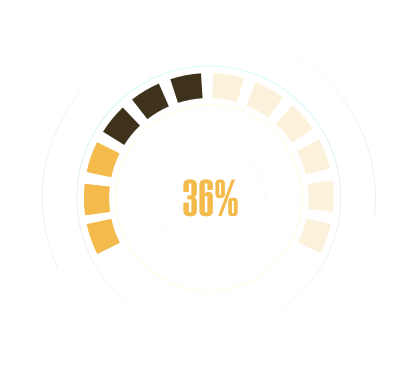
of successful attacks on coding agents ended in remote code execution
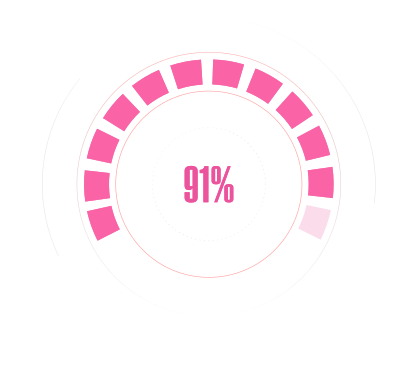
of successful attacks on productivity and consumer agents ended in silent data exfiltration
EVERY AGENT YOU BUILD. EVERY AGENT YOUR WORKFORCE USES.
Builders
Custom applications, agent frameworks, LLM gateways, and cloud agent platforms.


Consumers
Coding agents, productivity agents, browser and SaaS agents, and the shadow agents nobody registered.


Straiker Platform
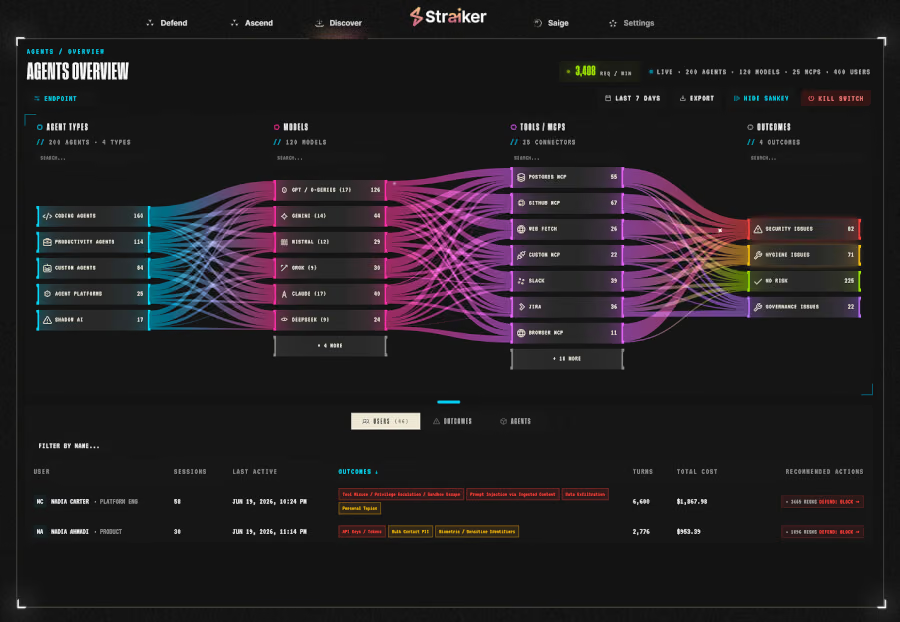
VISIBILITY AND GOVERNANCE
Frictionless discovery across endpoints, APIs, gateways, SaaS, and inference hooks
Maps agents to the models, tools, MCPs, Skills, data, permissions, and systems behind them
Surfaces risky permissions, unsanctioned connections, and malicious components
Blocks or revokes risky MCP and tool access directly


AI ADVERSARIAL TESTING
Reports real impact: remote code execution, data exfiltration, tool abuse, unauthorized actions
Highest attack success rate in the industry
New STAR Labs research becomes a production evaluation as it lands
Every finding becomes a Defend AI policy recommendation


AGENTIC RUNTIME DEFENSE
Detects remote code execution, file access violations, suspicious outbound access, destructive commands, and data exfiltration
Detect or Protect modes, with policies you write yourself
Protects agents across models, frameworks, clouds, gateways, and architectures
SaaS or on premises for regulated and sovereign environments


TAKE ROGUE OR COMPROMISED AGENTS OFFLINE IN SECONDS.
Take control of a compromised agent. Stop one, or stop your entire agentic estate.
Cut off tool access
Suspend the session
Isolate the agent
Stop one agent or many
Take the agent offline
Preserve the evidence
WHAT SECURITY AND AI TEAMS GET WITH STRAIKER
Turn attacks into runtime protection
Every successful Ascend AI attack can become a Defend AI policy, connecting continuous adversarial testing directly to runtime protection.
Contain rogue AI agents in seconds
Stop a compromised or rogue AI agent, cut off what it can access, or contain multiple agents without taking the rest of your agentic estate offline.
Secure every AI agent you build or use
Protect custom agents your teams build and the coding, productivity, SaaS, and shadow AI agents your workforce uses, all from the same platform.
Get audit-ready evidence for AI agent security
Keep agent inventory, full agentic traces, adversarial testing history, and policy logs mapped to OWASP, MITRE ATLAS, NIST AI RMF, and the EU AI Act.
THE RESEARCH UNDERNEATH IT ALL
STAR Labs is Straiker's AI and security research team. Its researchers work with frontier AI labs, which gives Straiker attack data on real agent behavior that is not available anywhere else. That research is the foundation of the product rather than an output of it. An attack STAR Labs finds on Monday becomes an Ascend AI evaluation and a Defend AI detection.
Research → Product → Protection
Join the Frontlines of Agentic Security
You're building and using AI agents because the business demands it. Straiker gives your security team the visibility, testing, and runtime protection to keep up, without becoming a blocker. Deploy fast. Stay secure.