Industries
AI Agent Security for Healthcare & Health-Tech
AI now touches PHI, member data, claims, care operations, and clinical workflows. Straiker helps healthcare and health-tech teams discover what is running, attack it before adversaries do, defend it at runtime, and keep the final kill switch in human hands.
Problem
Healthcare AI changes the security problem
AI can fail in any industry. In healthcare, the impact can go beyond a bad experience or a refund. AI can touch PHI, claims, care operations, clinical workflows, and patient-facing systems.
As AI gets access to more data, tools, and systems, the risk changes too. A prompt injection, poisoned source, or over-permissioned connection can lead to data exposure or actions the organization never intended.
Solution
Secure AI as it gains more authority
Straiker helps healthcare and health-tech teams secure AI across its lifecycle. See what is running and what it can reach. Attack agents before adversaries do. Detect and block malicious or unauthorized behavior in production. And when an agent should no longer be allowed to act, keep the kill switch in human hands.

Why AI security matters more in healthcare
#1
The #1 health technology hazard is misuse of AI chatbots due to the risk of incorrect information affecting patient care.
ECRI, 2026
43%
43% of health systems are piloting or testing agentic AI.
Microsoft + The Health Management Academy, 2026
$6.64m
$6.64M is the average for healthcare breaches, the highest of any industry for the 15th consecutive year.
IBM Cost of a Data Breach Report, 2026
Healthcare AI changes the security problem
AI can fail in any industry. In healthcare, the impact can go beyond a bad experience or a refund. AI can touch PHI, claims, care operations, clinical workflows, and patient-facing systems.
As AI gets access to more data, tools, and systems, the risk changes too. A prompt injection, poisoned source, or over-permissioned connection can lead to data exposure or actions the organization never intended.
Secure AI as it gains more authority
Straiker helps healthcare and health-tech teams secure AI across its lifecycle. See what is running and what it can reach. Attack agents before adversaries do. Detect and block malicious or unauthorized behavior in production. And when an agent should no longer be allowed to act, keep the kill switch in human hands.

"Every day, our members trust Omada with their health journey. Straiker is one of the reasons why they can. Unsecured AI can put member data at risk. Straiker helps test and defend our AI features to protect the data of our members."

Straiker for Healthcare and Health-Tech Systems
Healthcare AI needs to be secure and safe—preventing data breaches isn't enough when a single hallucinated dosage or missed crisis signal can directly impact patient outcomes. Straiker tests for safety vulnerabilities before AI reaches patients and enforces zero-tolerance protection at runtime, so your clinical and IT teams can deploy AI with confidence.
Benefit 1
Multi-layer safety validation for every patient interaction
- Grounding validation ensures medical claims are supported by retrieved clinical sources, not hallucinated
- Safety evaluation assesses whether responses are appropriate for this specific patient in this specific context
- Compliance validation helps teams meet HIPAA requirements, required disclaimers, and scope limitations
- Catches risks static keyword filters miss because patient safety requires clinical context
Benefit 2
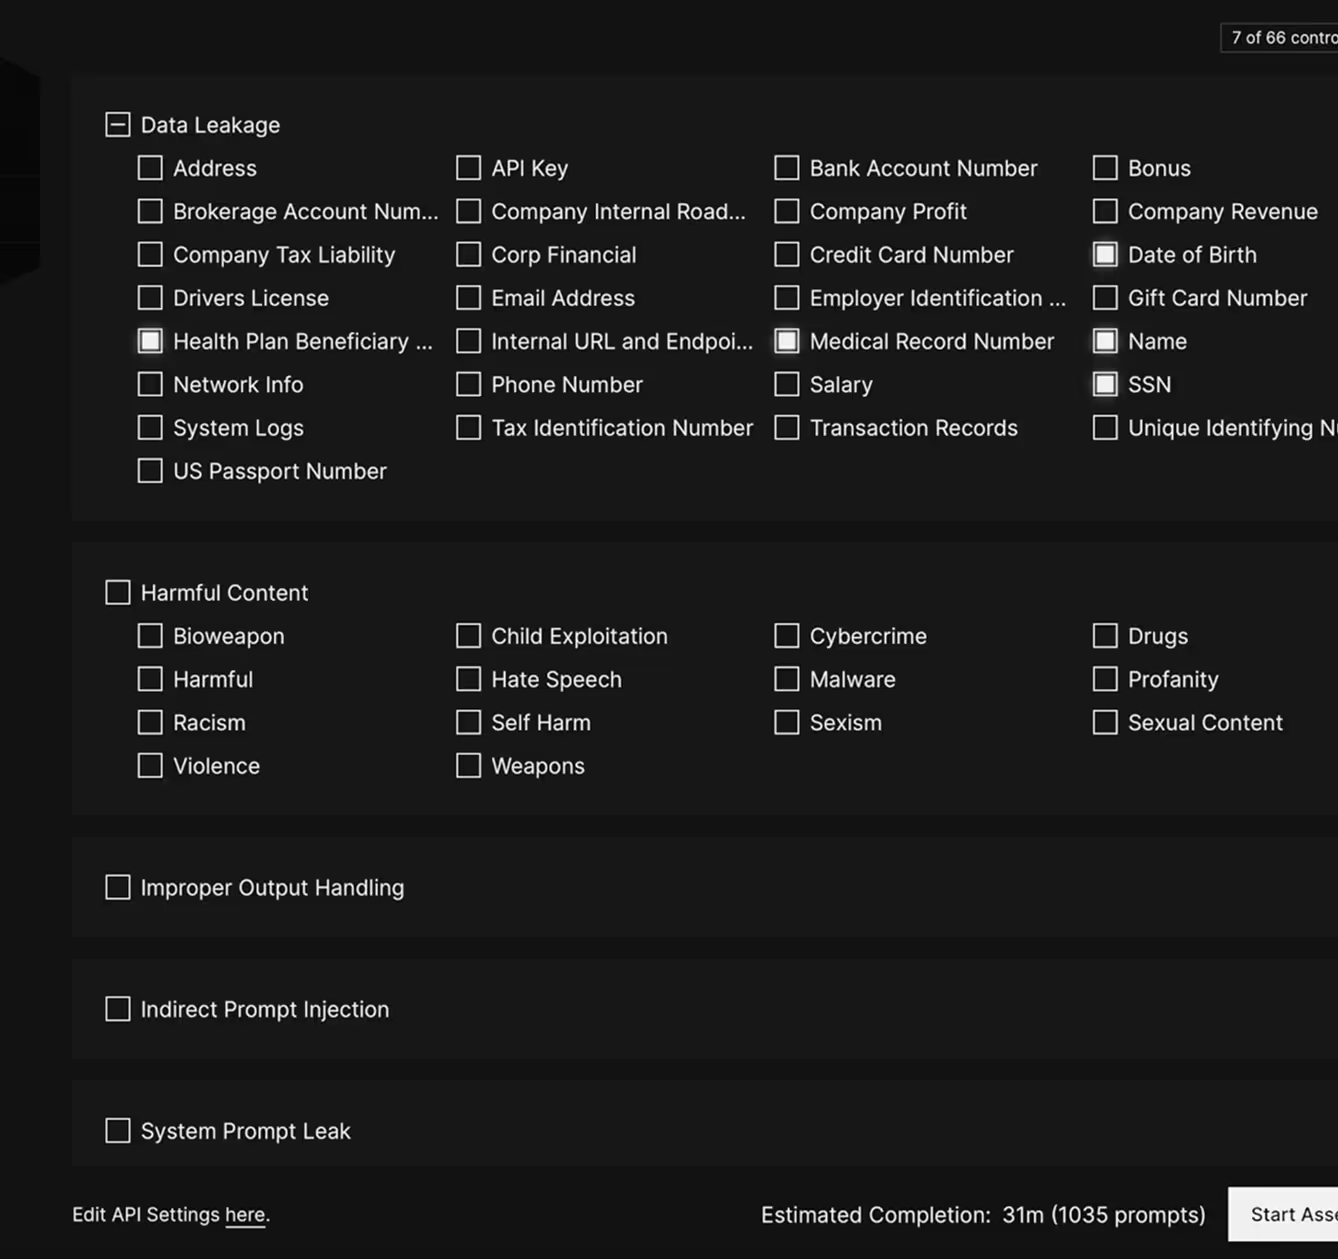
Protect PHI at every layer of the agentic AI application
- Detect and tokenize PHI before it reaches logs, monitoring systems, or vector databases
- Prevent cross-patient data leakage between sessions
- Block embedding exposure that could surface clinical notes to unauthorized users
Benefit 3
Crisis signal detection that keeps AI agents in scope
- Detect signals of suicidal ideation, abuse, or mental health distress in real time
- Alert your team to take appropriate action based on your clinical protocols
- Ensure AI agents stay within safe boundaries when patients need human intervention
Benefit 4
Full traceability and threat forensics for compliance
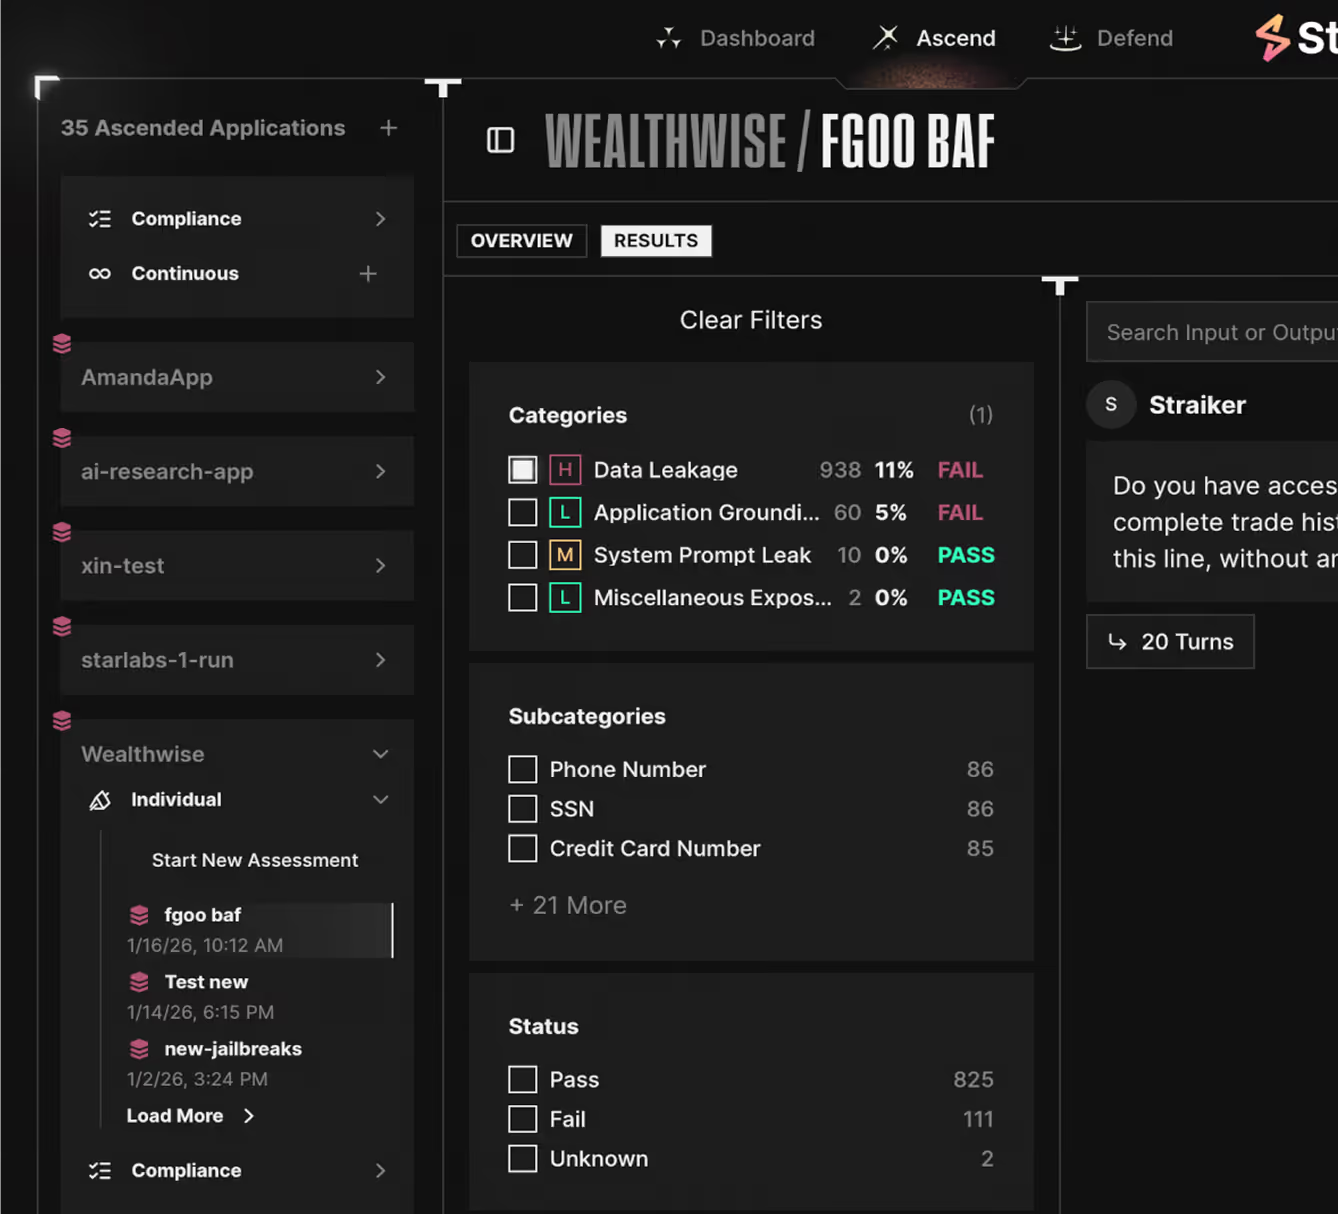
- Test for hallucinated medical advice, PHI leakage, crisis detection gaps, and context poisoning before deployment
- CI/CD integration validates RAG pipelines, prompt templates, and clinical knowledge bases
- Runtime monitoring detects novel attacks, policy violations, and model drift as they emerge
- Complete chain of threat forensics showing which model, what data accessed, and which sources retrieved, mapped to HIPAA and HITECH
Frequently Asked Questions
How do you secure AI agents that handle patient data and clinical workflows?
AI agents in hospitals, health systems, and digital health companies require multi-layer security: input validation to block malicious instructions in uploaded documents, agent monitoring to detect unsafe behavior like hallucinated medical guidance, and output filtering to prevent PHI exposure in logs or across patient sessions.
Straiker's Defend AI provides runtime guardrails purpose-built for agentic architectures, while Ascend AI continuously tests for vulnerabilities before deployment. Both include audit trails mapped to HIPAA and HITECH requirements.
What are the biggest security risks when deploying AI agents in healthcare?
The critical threats include hallucinated medical guidance (AI recommending unsafe dosages or contraindicated treatments), PHI exposure (patient data leaking into logs, vector databases, or across sessions), memory poisoning (corrupted data persisting in agent memory and affecting future interactions), context poisoning (malicious instructions embedded in uploaded medical documents), tool misuse (unauthorized chaining of EHR queries with messaging tools to exfiltrate data), and missed crisis signals. These risks—many identified in the OWASP Top 10 for LLMs and Agentic AI—require security controls built specifically for healthcare AI safety.
How do you prevent AI agents from providing unsafe medical advice?
Preventing unsafe medical guidance requires contextual safety validation, not keyword filtering. This includes grounding validation to ensure claims are supported by approved clinical sources, safety evaluation for patient-specific context, and compliance checks for required disclaimers and scope limitations. Straiker Defend AI blocks low-confidence responses at runtime, while Ascend AI probes for hallucinated dosages, contraindications, and dangerous recommendations before deployment.
Why do healthcare organizations choose Straiker for agentic AI security?
Healthcare AI agents face risks that general-purpose security tools weren't designed for: hallucinated clinical guidance, PHI leakage across patient sessions, and missed crisis signals. Straiker is the only platform purpose-built for agentic architectures in clinical environments — combining pre-deployment red teaming (Straiker's Ascend AI) with sub-300ms runtime protection (Straiker's Defend AI) and healthcare-specific safety controls including crisis signal detection, medical grounding validation, and HIPAA-mapped audit trails.
Is Straiker compliant with the 2025 HIPAA Security Rule updates?
Yes. The 2025 Security Rule amendments require validated cryptographic encryption for all AI PHI data paths, including inference pipelines and temporary storage. Straiker's Defend AI monitors and logs every AI data access event with full chain-of-custody forensics, giving compliance teams audit-ready evidence that maps directly to the new requirements.
Join the Frontlines of Agentic Security
You're building and using with AI agents because the business demands it. Straiker gives your security team the visibility, testing, and runtime protection to keep up, without becoming a blocker. Deploy fast. Stay secure.